Distinctive Cyber Security
Beazley Security is a cyber security services company with a unique perspective on risk management.
With deep roots in the cyber insurance industry, Beazley Security leverages firsthand experience from thousands of real-life incidents and claims each year to offer unparalleled insight into the evolving cyber threat and risk landscape. This expertise ensures that our approach is comprehensive—optimizing technical and organizational defenses while preparing and training teams to respond swiftly and effectively when needed.
These capabilities can be leveraged proactively to establish, test, or enhance a cyber security program; selectively to target a specific need; or reactively to respond to an active threat situation. Regardless of the need, Beazley Security has the depth to deliver value-adding expertise and the flexibility to work in terms that are well suited to the industry, regulatory, and business needs of our clients.
Full Spectrum Cyber
The combination of Beazley’s risk management services with Beazley Security’s expertise delivers an integrated cyber ecosystem spanning Insurance, Incident Response & Security.
Our Full Spectrum Cyber approach builds resilience across the entire risk life cycle, insulating your organization against financial, operational, and reputational damage.
Beazley Security Capabilities
In addition to providing comprehensive support for Beazley cyber insurance clients, we offer specialized services designed to strengthen your organization’s cyber security posture.
Our expertise is informed by insights from handling thousands of security incidents annually, helping ensure comprehensive protections across your threat landscape.


Incident Response & Restoration
Beazley Security’s “follow the sun” Incident Response teams are built to respond to potential and confirmed security events with the speed and precision necessary for analysis, containment, and recovery. Our approach is guided by scenario planning and documented procedures, ensuring a swift, effective response when breaches occur. This methodology is further driven by real-time threat intelligence, gained from responding to thousands of incidents and continuously updated from prime external sources.
When an incident occurs, Beazley Security experts provide a thorough digital forensic analysis using advanced tools in memory, network, and file system forensics to uncover the cause and extent of the breach. Our capable team will help restore business operations and expedite recovery, then can work with you to strengthen your security posture and proactively assess additional potential threats.

Beazley Security MXDR
With uncomplicated endpoint-based pricing that includes unlimited data ingestion and 90-day (standard) data retention, Beazley Security’s Managed eXtended Detection and Response (MXDR) service provides clients around-the-clock protection while delivering a cost-effective alternative to developing in-house cyber security capabilities.
Beazley Security MXDR leverages human intelligence with advanced technologies and external data sources to enable comprehensive coverage.
Dive deeper into our MXDR offering
Why organizations need Exposure Management
Traditional vulnerability management tools were not designed for the scale and complexity of today’s expanding attack surface. Organizations using such tools often focus on identifying vulnerabilities within known assets through aggressive scanning to show internal hygiene gaps.
However, this approach tends to break down when relying on predefined asset inventories, which quickly become outdated as environments evolve.
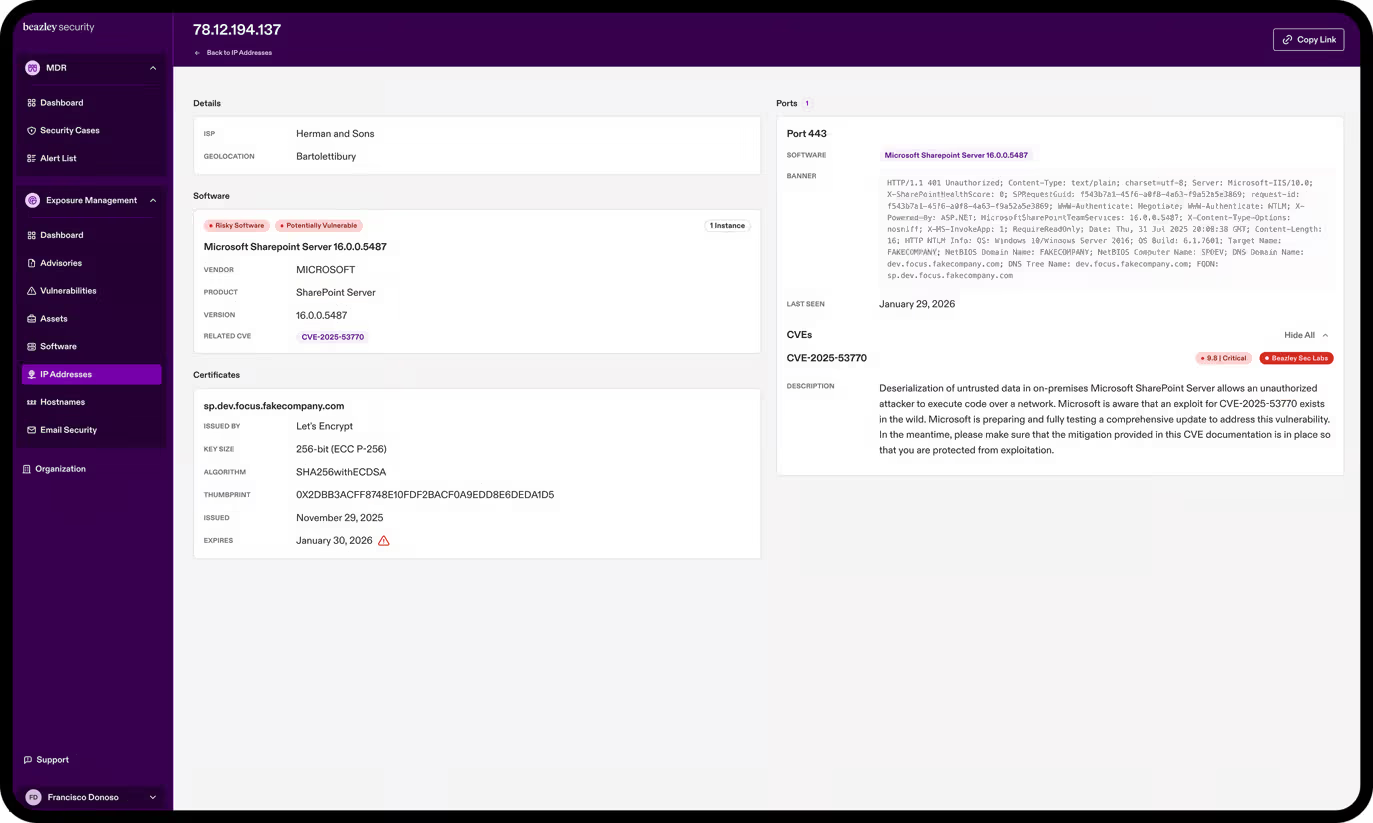
Beazley Security’s Exposure Management is the evolution of vulnerability management, providing a continuous, external view of your attack surface. The platform identifies what is actually exposed and exploitable, automatically discovering both known and unknown internet-facing assets from an attacker’s perspective. Instead of relying on severity scores alone, Exposure Management prioritizes risks based on real-world exploitability, leveraging Known Exploited Vulnerabilities (KEVs) and intelligence from Beazley Security Labs to reduce noise and focus on the exposures that matter most.
How Exposure Management outperforms vulnerability management tools
Traditional VM tools
Beazley Security Exposure Management
Exposure Management platform capabilities
Automate asset discovery & tracking
Discover, identify, and track publicly accessible assets across your monitored domains automatically as your environment evolves. This includes subdomains, IP addresses, hosting environments, exposed services, open ports, and externally accessible software.
Enrich findings with threat context
Correlate findings with Known Exploited Vulnerabilities (KEVs), Risky Software, and active attacker campaigns curated by Beazley Security Labs to prioritize exposures based on real-world attack behavior.
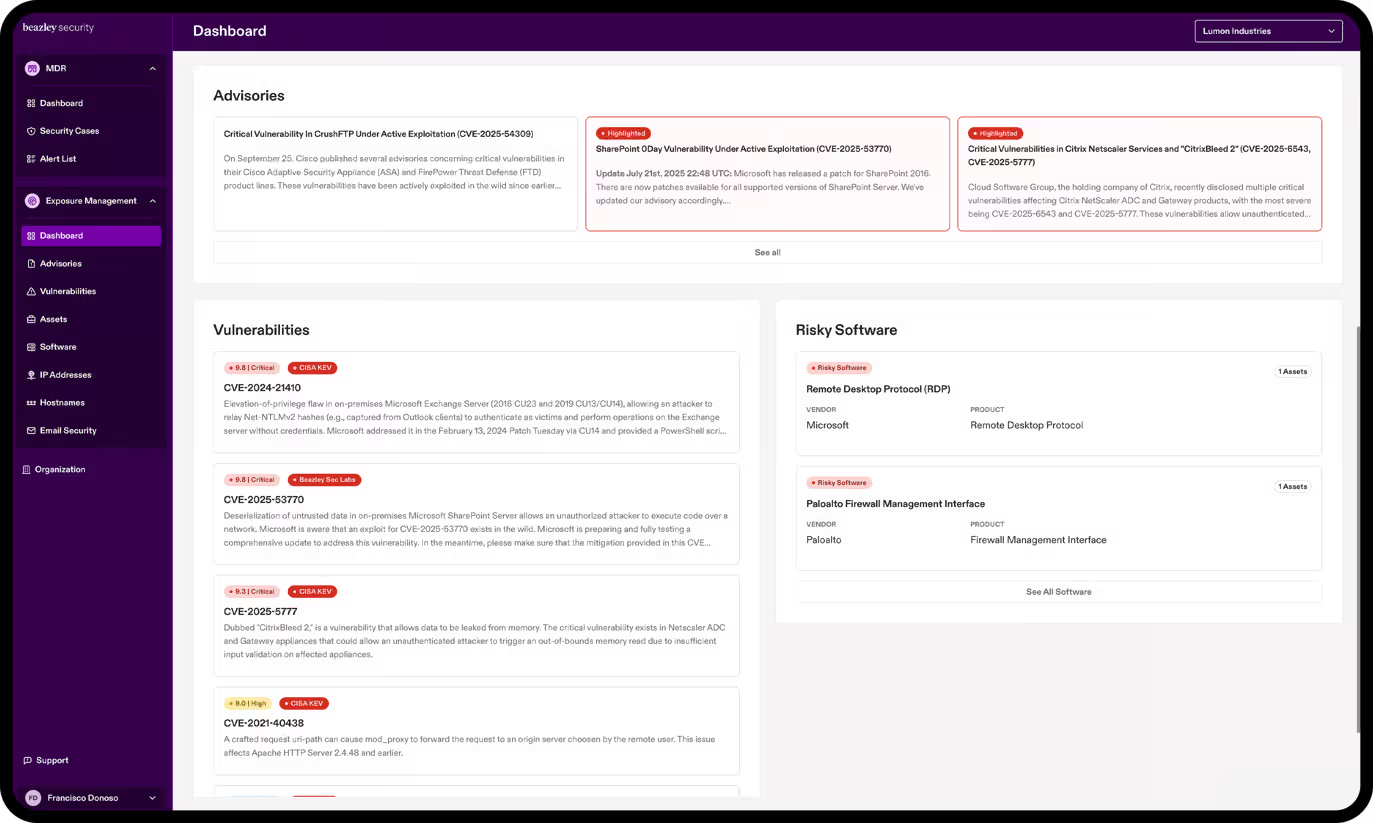
Identify emerging threat exposure
Monitor threat intelligence and Incident Response (IR) data to continuously track emerging threats. When vulnerabilities are confirmed to be actively exploited or Beazley Security Labs publishes a new advisory tied to an observed attack campaign, the platform updates its detection logic to automatically identify impacted assets and notify you of exposures.
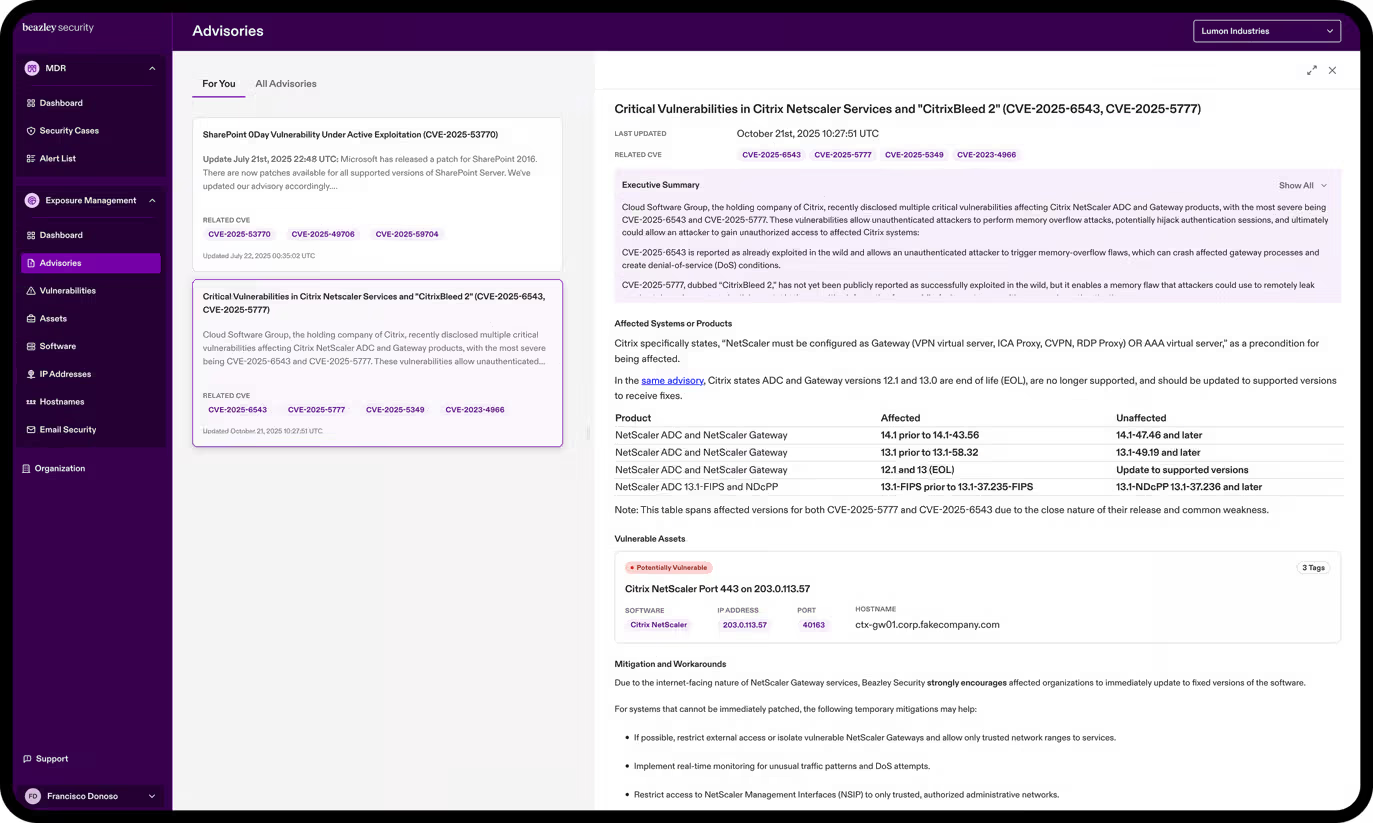
Prioritize based on real-world risks
Rank exposures based on real-world exploitability, observed attacker behavior, and active threat activity rather than abstract severity scoring or theoretical risk models. Exposure Management helps teams focus on what’s exposed, fix what matters, and stay ahead of risk.
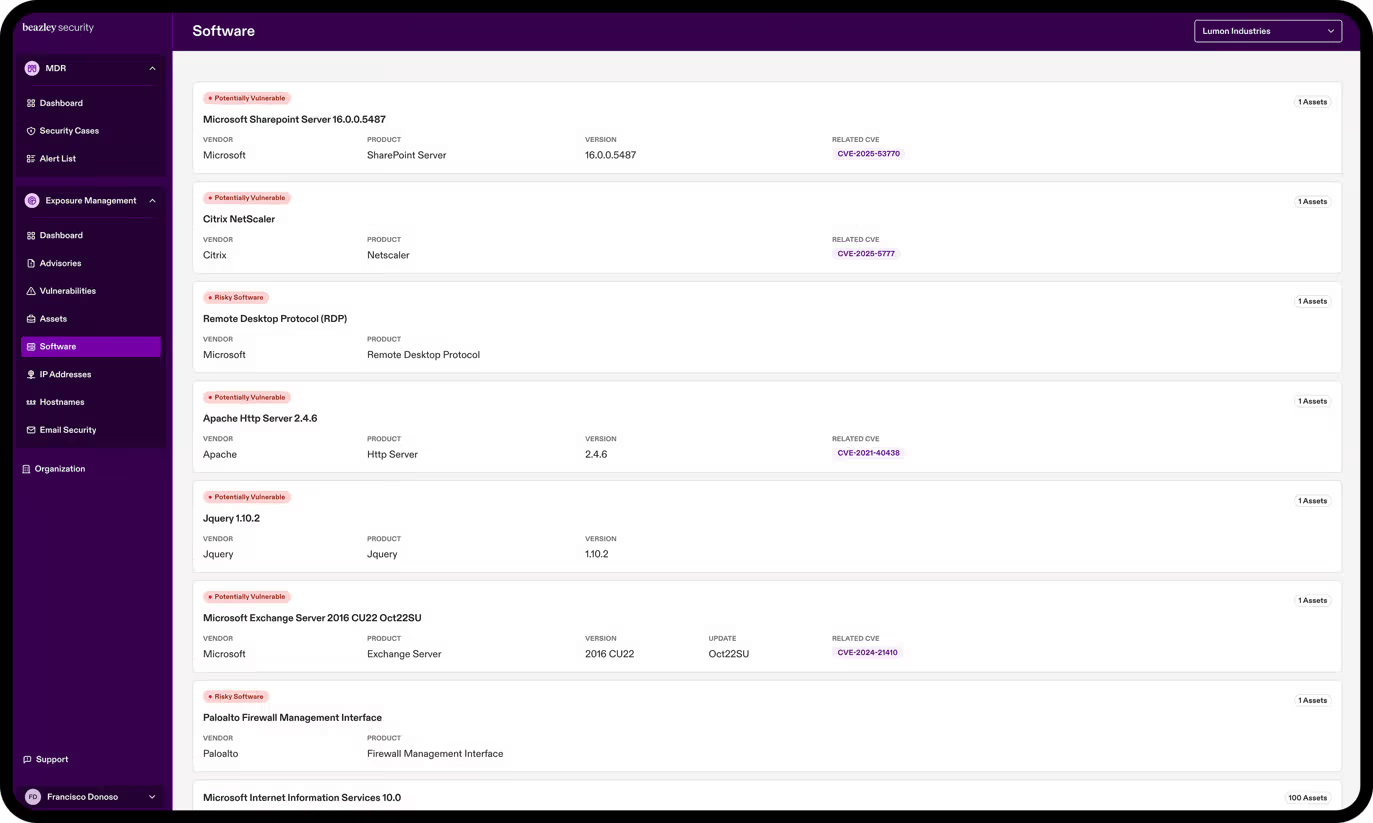
Validate exposures & track risks
Visualize with native dashboards and reporting capabilities to identify exposure trends over time, track outstanding risk, and continuously validate exposure so it doesn’t reappear as your environment evolves.
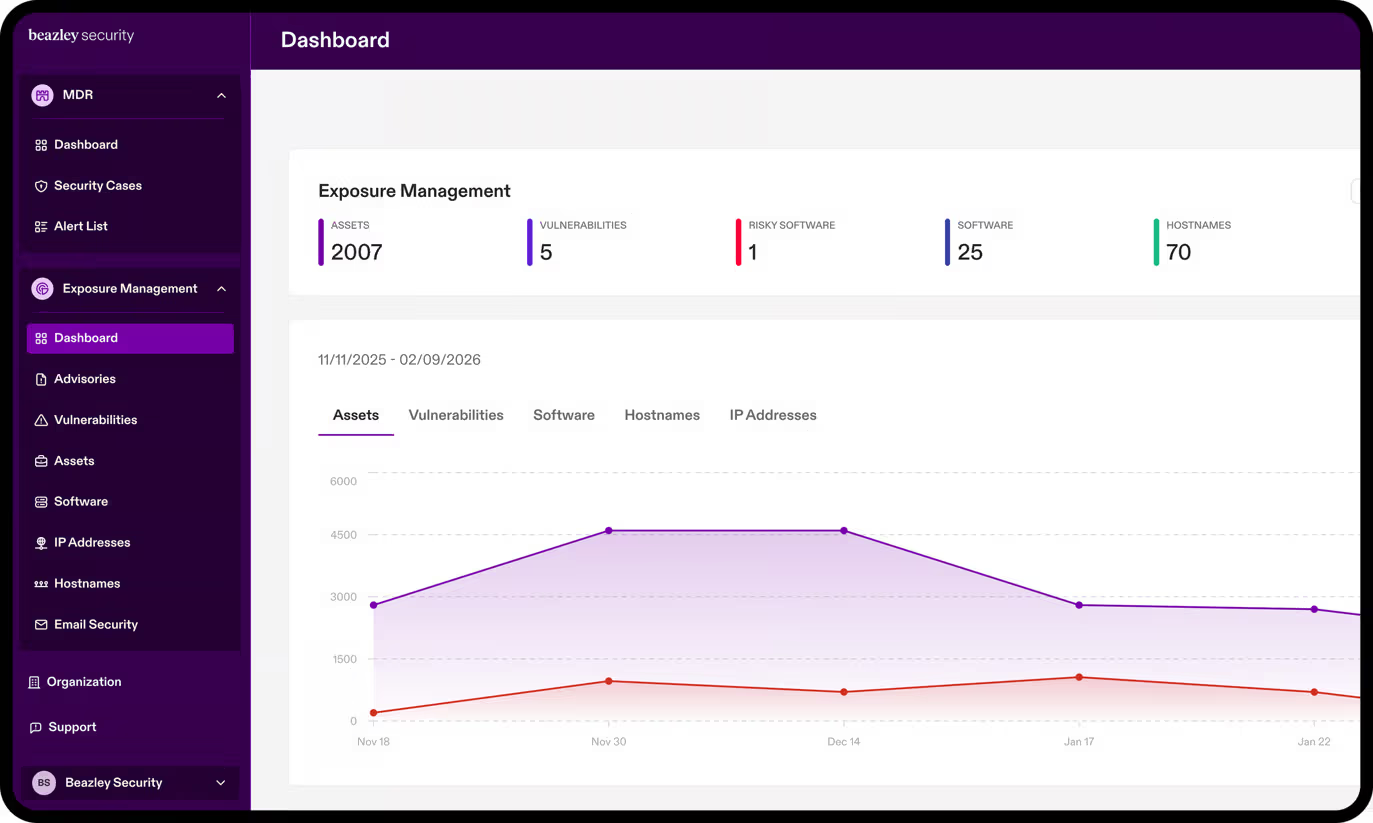
See your external attack surface through a new lens
We follow the sun
With offices strategically located around the world, Beazley Security ensures our global team is always available to support and safeguard your business, no matter where you operate.